
Security and Compliance Requirements
On this page
In this lesson, you will learn:
- The security questions Discovery raises
- SNWR’s security rules
- Why to capture them before design
🔁 Quick look back: Last time: Who Uses the CMDB Data, and How. You learned how data users decide which classes and fields matter.
1 The Problem: Security Rules Arrive Too Late
On many projects, security reviews the design after it’s built. Then:
- Accounts are rejected for having too many rights.
- Scan times clash with security monitoring.
- Work is redone.
👉 The fix: Capture security rules as requirements now, before design.
2 Common security requirements
- Least privilege: accounts get only the rights they need.
- Scan windows outside business hours.
- Password and key rotation.
- Audit trail: who changed schedules, and when.
- MID Server hardening.
Key term: Least privilege
Give an account only the rights it needs, and nothing more.
3 Why now
Security rules change the design: which accounts, which MID Server hosts, which times. So they must come before design.
⭐ Remember: Farah is an approver. Treat her rules as requirements, not opinions.
4 Project Clear View: How We Implemented It
📍 Situation: Farah joined the security workshop with a list of concerns.
🧭 Decision: Turn her concerns into written requirements before design.
🛠️ Steps we took:
- Walked through accounts, scan times, rotation and audit with Farah.
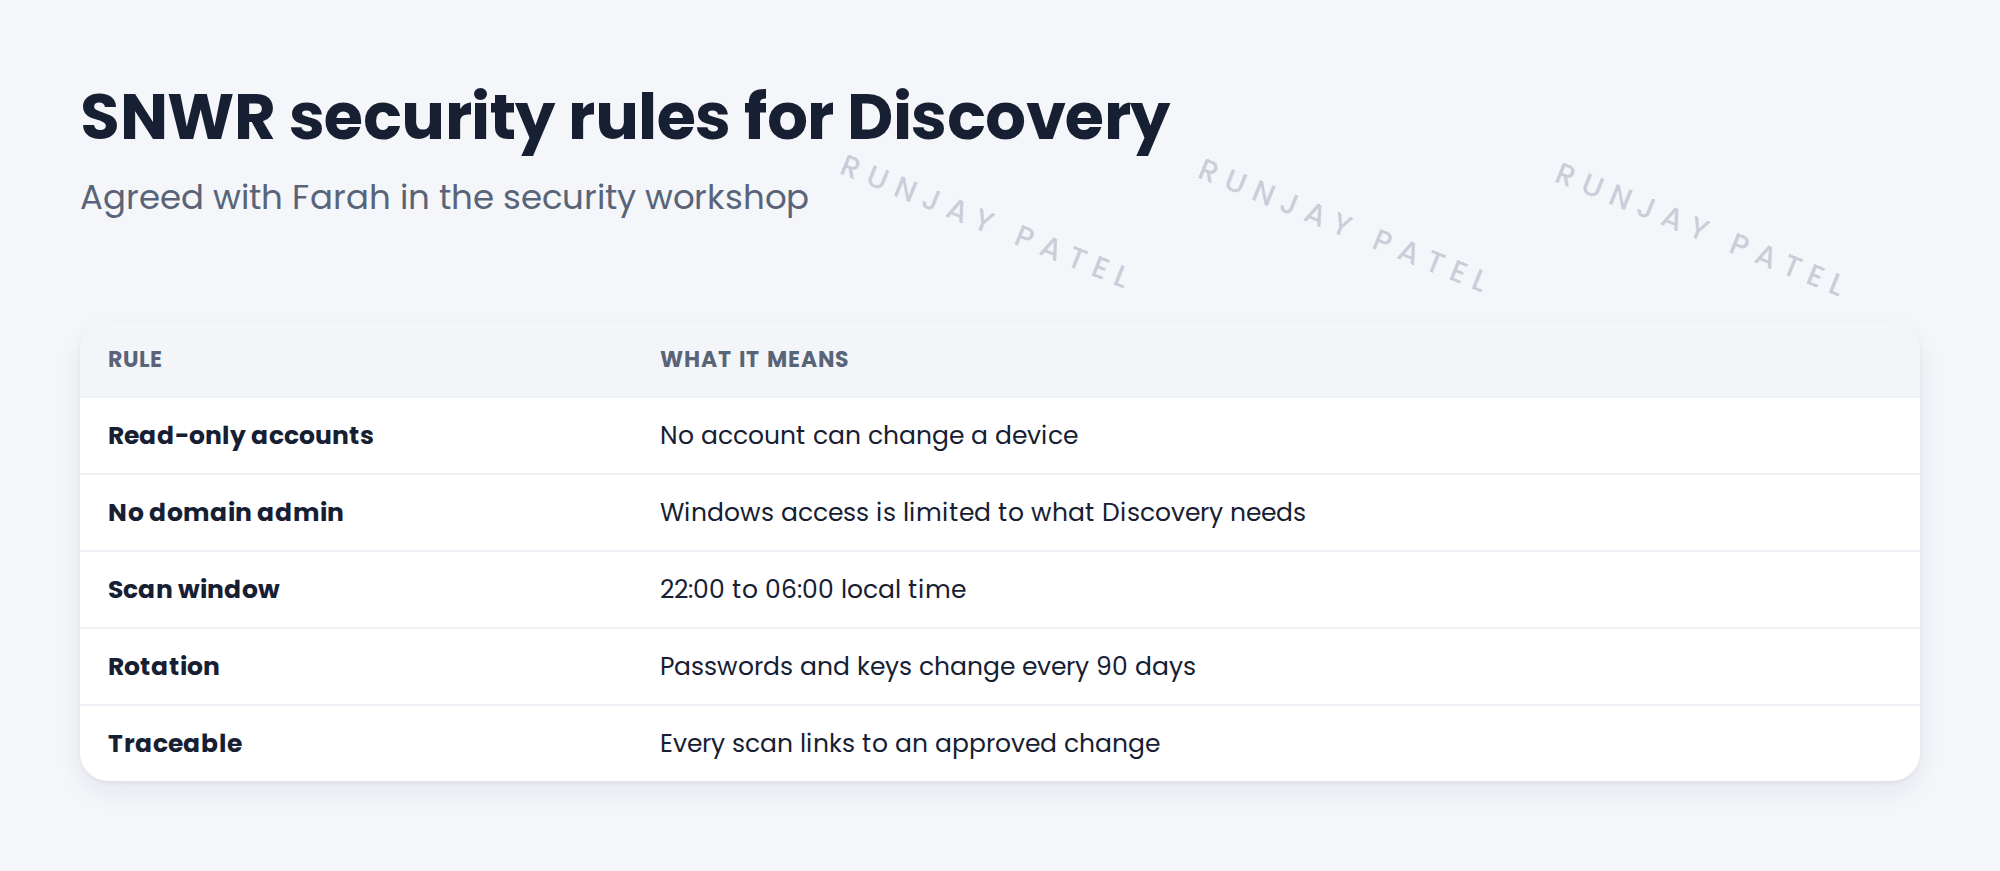
- Wrote five rules as requirements.
- Asked her to prioritise: all five are must-have.
- Linked each rule to the design area it affects.
✅ What we verified:
- Farah approved the wording of all five rules.
- Each rule is linked to a design decision.
📁 Evidence: The security section of the requirements, signed by Farah.
5 Quick recap
- Capture security rules before design.
- Common rules: least privilege, scan windows, rotation, audit.
- SNWR’s scan window is 22:00 to 06:00 local time.
- Treat security rules as requirements.
6 Check yourself
Think of your answer first. Then tap to check.
1 What does least privilege mean? Show answer
An account gets only the rights it needs, and nothing more.
2 What is SNWR’s scan window? Show answer
22:00 to 06:00 local time.
3 Why capture security rules before design? Show answer
They change the design, so learning them late means redoing work.
Nice work! SNWR’s security rules are part of the requirements. 🎉
Next up: Defining Acceptance Criteria
Was this lesson helpful?
Please log in to share lesson feedback.
Have a question or doubt?
Ask here and get help from instructors and fellow learners.
Only logged-in learners can post.