
Discovery Methods: IP-Based, Cloud API, ACC and Credential-less Options
On this page
In this lesson, you will learn:
- The four ways Discovery can find things
- When to use each one
- Which method each SNWR zone uses
🔁 Quick look back: Last time: How Discovered Data Reaches the CMDB. You learned how IRE checks discovered data before it writes a CI.
1 The Problem: One Method Can’t Reach Everything
IP-based scans work well for the Mumbai server zone. But SNWR has other places:
- The AWS account has no servers you can SSH to from Mumbai.
- The Finance zone blocks all inbound connections.
- Some unknown devices have no credential at all.
👉 The fix: Learn the four methods, and pick the right one for each zone.
2 The four methods
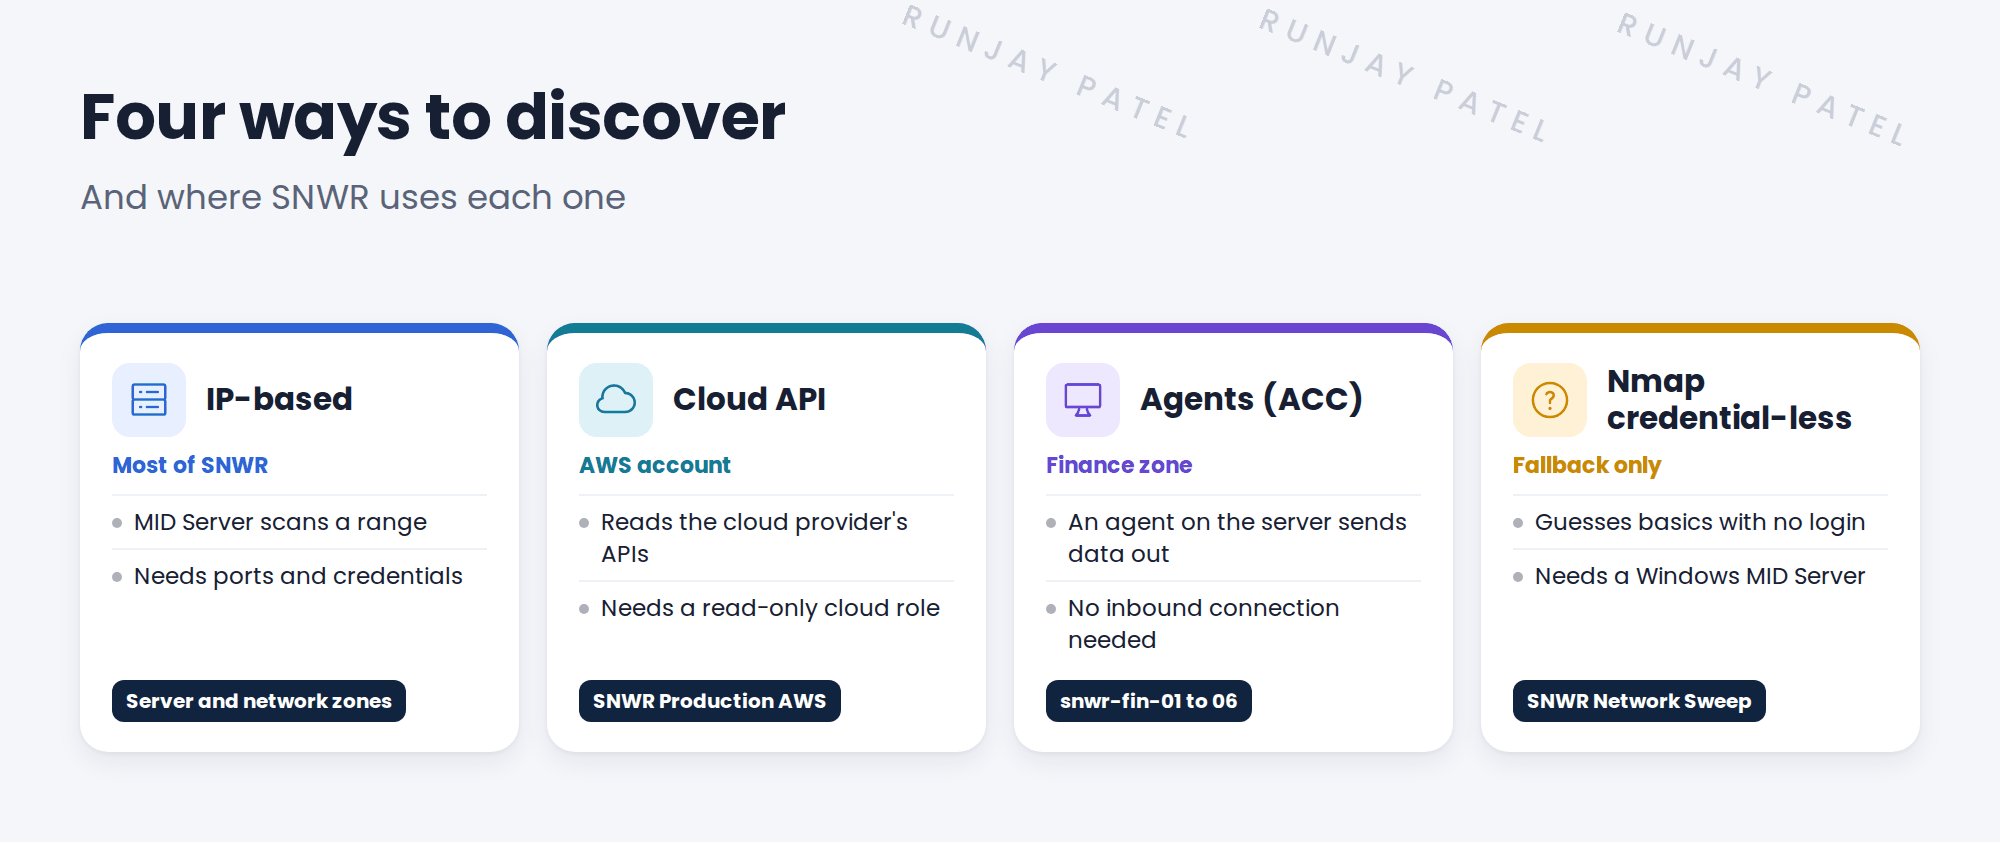
- IP-based Discovery. A MID Server scans a range and logs in to each device. The main method.
- Cloud Discovery. A MID Server reads the cloud provider’s APIs, such as AWS. No IP scan of the cloud needed.
- Agent Client Collector (ACC). A small agent runs on the server and sends data out. Good for locked-down zones.
- Nmap credential-less Discovery. When no login works, a Windows MID Server with Nmap can still guess basic facts. It’s a fallback, not a plan.
⚠️ Don’t confuse: Nmap credential-less Discovery and ACC are very different. One guesses from outside with no login. The other runs inside the server. Don’t mix them up.
3 Choosing a method
| If the target is… | Use |
|---|---|
| Reachable from a MID Server, with a login | IP-based Discovery |
| In a public cloud account | Cloud Discovery |
| In a zone that blocks inbound connections | ACC agents |
| Unknown, with no credential, on a trusted network | Nmap credential-less (fallback only) |
4 Project Clear View: How We Implemented It
📍 Situation: SNWR’s zones need different methods, and the team keeps asking ‘will a scan work there?’.
🧭 Decision: Pick one main method per zone, and write down why.
🛠️ Steps we took:
- Chose IP-based Discovery for both server zones and all network zones.
- Chose Cloud Discovery for SNWR Production AWS.
- Chose ACC agents for the Finance zone, because it blocks inbound connections.
- Allowed Nmap credential-less only in SNWR Network Sweep, to spot unknown devices.
✅ What we verified:
- Farah agreed with agents for Finance.
- Everyone could say which method covers which zone.
📁 Evidence: A first draft of design decision DD-D02 (see Solution Design › Choosing the Discovery Method for Each Zone).
5 Quick recap
- IP-based Discovery is the main method, using MID Servers and credentials.
- Cloud Discovery reads cloud APIs.
- ACC agents send data out, so they suit locked-down zones.
- Nmap credential-less Discovery is only a fallback.
6 Check yourself
Think of your answer first. Then tap to check.
1 Which method suits SNWR’s Finance zone, and why? Show answer
ACC agents, because the zone blocks all inbound connections. The agents send data out.
2 Is Nmap credential-less Discovery the same as ACC? Show answer
No. Nmap guesses basics from outside with no login. ACC is an agent running on the server.
3 How is the AWS account discovered? Show answer
With Cloud Discovery, which reads the AWS APIs through a MID Server.
Nice work! You can pick the right method for each part of a network. 🎉
Next up: Where a Discovery Implementer Works in ServiceNow
Was this lesson helpful?
Please log in to share lesson feedback.
Have a question or doubt?
Ask here and get help from instructors and fellow learners.
Only logged-in learners can post.