
Hardening the MID Server
On this page
In this lesson, you will learn:
- Why the MID Server is a security target
- Farah’s hardening checklist
- How to prove it’s done
🔁 Quick look back: Last time: MID Server Sizing, Threads and Performance. You learned how size, memory and threads affect scan speed.
1 The Problem: A MID Server Holds the Keys to the Network
The MID Server uses Discovery credentials to reach every server. If someone takes over the host:
- They could misuse its access.
- They could read its logs and settings.
👉 The fix: Harden every MID Server host to Farah’s checklist.
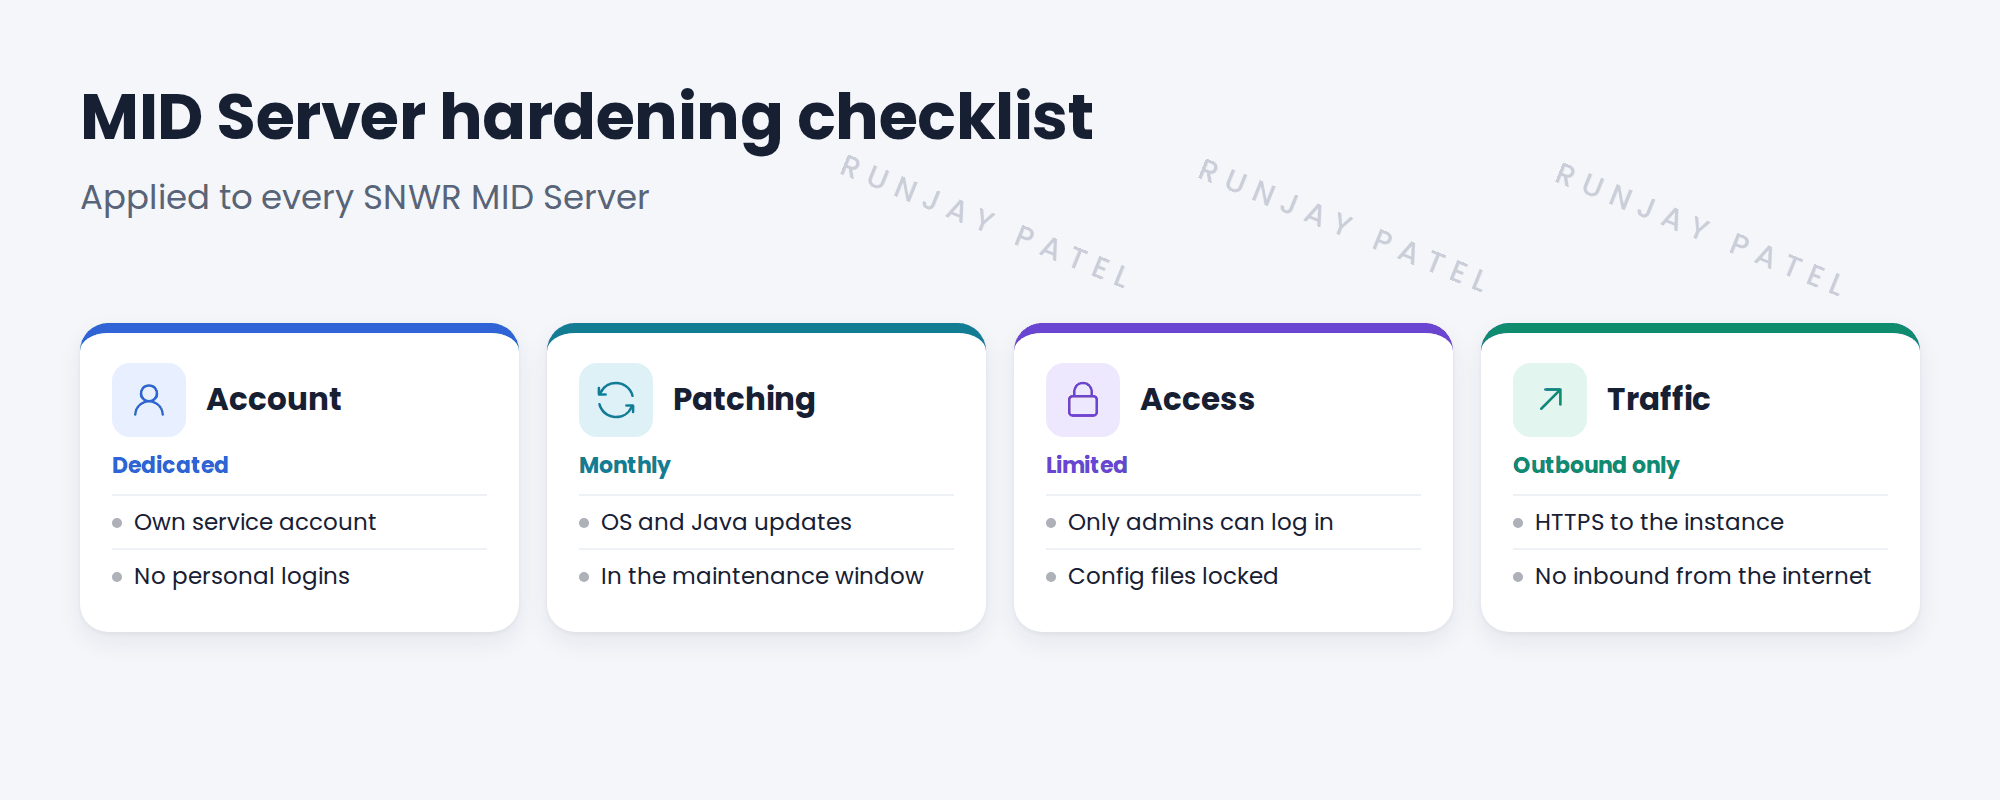
2 The checklist
- A dedicated service account runs the MID Server.
- The host is patched on a schedule.
- Only a few admins can log in.
- Config and log folders are locked down.
- Only outbound HTTPS to the instance.
- Antivirus excludes MID folders only as documented.
3 Proving it
Ask the host owner for evidence: account settings, patch dates and access lists. Keep them with the readiness evidence.
⭐ Remember: Hardening isn’t a one-time task. It becomes part of operations.
4 Project Clear View: How We Implemented It
📍 Situation: Farah asked for proof the MID hosts are safe.
🧭 Decision: Apply her checklist to every MID host and collect evidence.
🛠️ Steps we took:
- Confirmed each MID runs as its own service account.
- Priya added the hosts to monthly patching.
- Limited logins to two admins.
- Collected evidence and sent it to Farah.
✅ What we verified:
- Farah accepted the evidence for all five hosts.
- Hardening checks are in the runbook.
📁 Evidence: Hardening evidence in the tracker.
5 Quick recap
- A MID Server holds powerful access, so protect it.
- Use a dedicated account, patching, limited access and locked config.
- Allow only outbound HTTPS to the instance.
- Keep evidence and repeat checks in operations.
6 Check yourself
Think of your answer first. Then tap to check.
1 Why is a MID Server a security target? Show answer
It uses credentials that reach every server.
2 Name three hardening steps. Show answer
Any three of: dedicated account, patching, limited logins, locked config, outbound-only traffic.
3 Is hardening a one-time task? Show answer
No. It continues in operations.
Nice work! SNWR’s MID Servers are hardened. 🎉
Next up: MID Server Health, Upgrades and Operations
Was this lesson helpful?
Please log in to share lesson feedback.
Have a question or doubt?
Ask here and get help from instructors and fellow learners.
Only logged-in learners can post.